

Publishing to npm
Publish your public-facing Fern TypeScript SDK to the npmjs
registry. After following the steps on this page,
you’ll have a versioned package published on npm. To distribute the SDK
internally instead, generate to the local file system (optionally
self-hosted) and build a tarball with
fern generate --package.
If you’re using token-based authentication, npm has deprecated long-lived classic tokens. See Migrating from token-based to OpenID Connect (OIDC) publishing to upgrade to the more secure OIDC authentication.
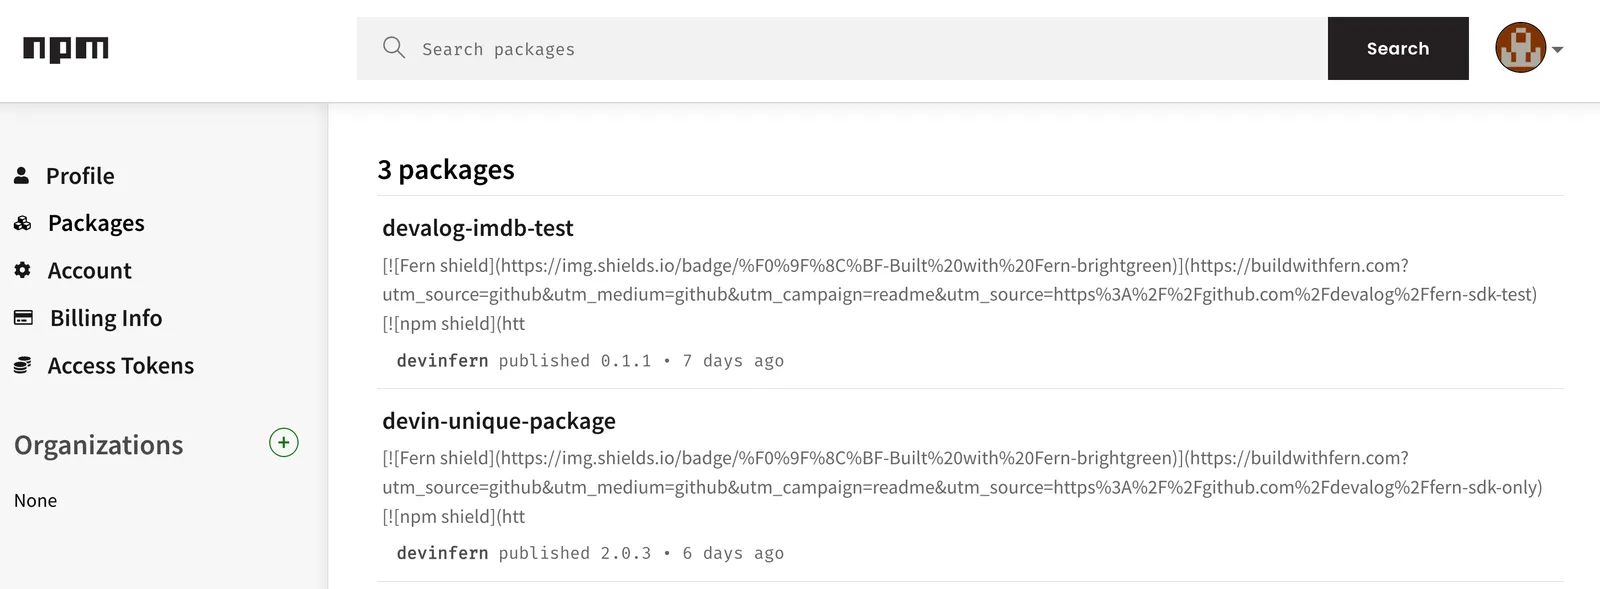
This page assumes that you have:
- An initialized
fernfolder, a GitHub repository for your TypeScript SDK, and a TypeScript generator group ingenerators.yml. See Generating an SDK (TypeScript).
Configure SDK package settings
Update your generators.yml file to configure the package name, output location, and client naming for npm publishing. Your generators.yml should live in your source repository (or on your local machine), not the repository that contains your TypeScript SDK code.
Configure output location
In the group for your TypeScript SDK, change the output location from local-file-system (the default) to npm to indicate that Fern should publish your package directly to the npmjs registry:
Configure GitHub publishing
Fern can automatically publish your SDK to npmjs via GitHub Actions. Configure your GitHub repository and publishing mode:
Optionally set the mode to control how Fern handles SDK publishing:
mode: release(default): Fern generates code, commits to the default branch (or thebranchyou specify), and tags a release automaticallymode: pull-request(recommended): Fern generates code and creates a PR for you to review before releasemode: push: Fern generates code and pushes to a branch you specify for you to review before release
You can also configure other settings, like the reviewers or license. Refer to the full github (generators.yml) reference for more information.
Configure authentication
Choose how you want to authenticate with npmjs when publishing.
npm has deprecated long-lived classic tokens for publishing from CI/CD workflows. OpenID Connect (OIDC) authentication is strongly recommended for security.
OIDC authentication (Recommended)
OIDC-based publishing (also known as “trusted publishing”) is the most secure way to publish. With OIDC, you don’t need to manage authentication tokens - npmjs trusts your GitHub repository to publish directly.
- Fern TypeScript SDK generator version
3.12.3or later - Fern CLI version
0.94.0or later (only required for local generation with--local)
Publish a placeholder package
OIDC can’t perform a package’s first publish: npm requires the package to exist before you can add a trusted publisher. Publish a placeholder version to create it:
Set the placeholder version to something below your first real release (for example, 0.0.0).
Authorize your repository on npmjs.com
Configure trusted publishing on npmjs.com to allow your GitHub repository to publish:
- Open the package page on npmjs.com and go to the Settings tab
- Find the Trusted Publisher section and click Add trusted publisher
- Select GitHub Actions as your provider
- Fill in:
- Organization or user: Your GitHub username or organization
- Repository: Your TypeScript SDK repository name (e.g.,
your-org/your-repository) - Workflow filename:
ci.yml - Environment name: Leave blank
- Under Allowed actions, select Allow
npm publish
Generate your SDK
Generate your SDK to create the GitHub Actions workflow with OIDC configuration:
This creates a .github/workflows/ci.yml file that’s configured to use OIDC for npm publishing. Alternatively, you can push your generators.yml changes and let the Fern GitHub Action generate the workflow for you.
Troubleshooting
“Unable to authenticate” error
Common causes:
- Workflow filename doesn’t match exactly (must be
ci.yml) - Trusted publisher configuration on npmjs.com doesn’t match your repository settings
- Using self-hosted runners (not supported by npmjs.org)
Solution: Double-check your trusted publisher configuration on npmjs.com matches your repository name and workflow filename exactly.
Private repository limitations
Provenance attestations aren’t generated for packages published from private repositories, even when using trusted publishing. This is a known limitation.
Token-based authentication (Legacy)
npm has deprecated long-lived classic tokens. Long-lived authentication tokens can be exposed in logs, compromised, and are difficult to manage and rotate. OIDC-based authentication is strongly recommended instead.
Generate an npm token
- Log into npmjs.com
- Click on your profile picture and select Edit Profile
- Select Access Tokens
- Click Generate New Token and choose either Classic Token (select “Automation” type) or Granular Access Token
- Save your token securely - it won’t be displayed again
Publish your SDK
Your SDK will automatically be published to npmjs when you create a GitHub release with a version tag:
- Create a GitHub release with a version tag (for example,
v1.0.0) - The CI workflow will run automatically and publish to npm
- View your package on npmjs.com to confirm the version
Alternative: Manual workflow dispatch
If you prefer to trigger publishes manually, create a .github/workflows/publish.yml file:
Add your FERN_TOKEN as a repository secret (run fern token to generate one), then trigger the workflow from the Actions tab.
Migrating from token-based to OIDC publishing
If you’re using token-based authentication and need to migrate to OIDC, follow these steps:
Why migrate to OIDC
npmjs is implementing trusted publishing to remove security risks associated with long-lived tokens, which can be:
- Exposed in logs or configuration files
- Compromised and used persistently until manually revoked
- Difficult to manage and rotate
OIDC-based publishing uses short-lived, cryptographically signed tokens that are specific to your workflow and can’t be extracted or reused.
Prerequisites
Before migrating, ensure you have:
- A package published to npmjs.org
- A GitHub repository with GitHub Actions configured
- Access to your package settings on npmjs.com
- Fern CLI version
0.94.0or later (for local generation)
Choose your migration path
Select the approach that fits your situation:
Path 1: Upgrade your generator (Recommended)
This is the easiest path if you can upgrade to version 3.12.3 or later of the TypeScript SDK generator.
When to use this path:
- You’re able to upgrade to Fern TypeScript SDK generator version 3.12.3 or later
- You haven’t
.fernignore’d your CI workflow file
Configure trusted publishing on npmjs.com
Follow npm’s “Add a trusted publisher on npmjs.com” instructions:
- Open the package page on npmjs.com and go to the Settings tab
- Find the Trusted Publisher section and click Add trusted publisher
- Select GitHub Actions as your provider
- Configure:
- Organization or user: Your GitHub username or organization
- Repository: Your TypeScript SDK repository name
- Workflow filename:
ci.yml(the default Fern workflow file) - Environment name: Leave blank (unless you use GitHub environments)
- Under Allowed actions, select Allow
npm publish
Update your generators.yml
Change the output.token field from ${NPM_TOKEN} to OIDC and ensure you’re using version 3.12.3 or later:
Regenerate your SDK
Regenerate your SDK with the updated CI configuration. You can do this either:
Locally:
Or via GitHub Actions:
If you use the Fern GitHub Action to generate your SDK, simply push your updated generators.yml file and let the workflow regenerate the SDK for you.
This will update your .github/workflows/ci.yml file with the required OIDC permissions.
Path 2: Manual CI workflow update
Use this path if you can’t upgrade the generator or have customized your CI workflow.
When to use this path:
- You can’t upgrade due to breaking changes or bugs
- You’ve customized your CI workflow and added it to
.fernignore - Path 1 didn’t update your workflow file
Configure trusted publishing on npmjs.com
Follow the same instructions as Path 1 to add your repository as a trusted publisher on npmjs.com.
Update your CI workflow manually
Open your .github/workflows/ci.yml file and make these changes to the publish job:
Key changes:
- Add
permissionsblock withid-token: writeandcontents: readto the publish job - Add step to update npm to version 11.5.1 or later
- Remove the
npm config setline from the publish step - Remove the
envblock withNPM_TOKENfrom the publish step
Verify your migration
After completing either migration path:
- Trigger a workflow run by creating a GitHub release with an alpha tag (for example,
v1.0.0-alpha) - Check the workflow logs to verify the publish step succeeds
- Verify provenance by visiting your package on npmjs.com - you should see a provenance badge
Migration troubleshooting
"Unable to authenticate" error
Common causes:
- Workflow filename doesn’t match exactly (must be
ci.ymlwith the.ymlextension) - Missing
id-token: writeorcontents: readpermissions in workflow - npm CLI version is older than 11.5.1
- Using self-hosted runners (not supported)
Solution: Double-check your trusted publisher configuration on npmjs.com matches your actual workflow file name and verify all requirements are met.
Workflow still using NPM_TOKEN
If your workflow continues using token-based authentication:
- Verify you’ve removed the
npm config setline and theenv: NPM_TOKENblock from the publish step - Check that npm CLI version 11.5.1+ is installed (add the update npm step)
- Ensure you’re using generator version 3.12.3 or later (if using Path 1)
- When using
--localgeneration, you need to use Fern CLI version 0.94.0 or later